Cold wallet manufacturer Trezor has issued an urgent alert urging users who purchased devices through distributor CryptoBilis since March to immediately transfer their funds. The warning comes after the discovery of an unauthorized circuit in a Trezor Safe 5 model sold in Southeast Asia.
The suspicion of physical tampering in the distribution chain highlights the risks of interception of crypto hardware, underscoring the importance of maintaining custody under the strictest technical and operational verification standards.
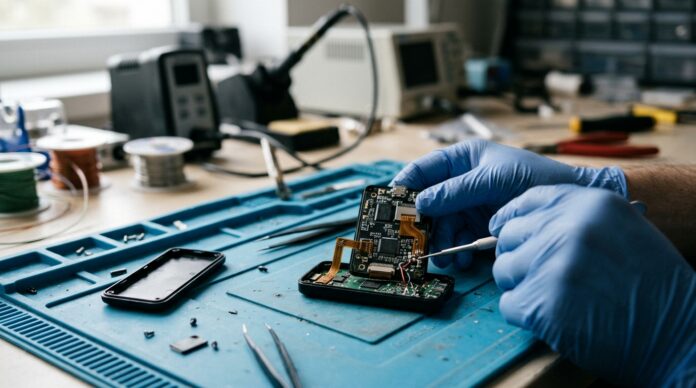
Trezor has urged its customers to take immediate precautions after receiving a technical report about a possible hardware implant in a Trezor Safe 5 device acquired through the reseller CryptoBilisAccording to data reported by a user in Indonesia through the e-commerce site Tokopedia during the month of August, the device contained an unauthorized printed circuit board capable of intercepting the information visible on the screen.
The attack vector: screen interception and mobile connectivity
Preliminary analysis indicates that the malicious circuit implanted within the physical wallet chassis was designed to record what is displayed on the device's screen. This critically includes the recovery phrase or backup seed at the exact moment the user first sets up their wallet. Subsequently, this spyware module could transmit the sensitive information via cellular connectivity to an external server controlled by remote attackers.
This method bypasses standard internal cryptographic integrity controls. The digital signature and original firmware remain intact and pass conventional cryptographic boot checks, since the implant does not alter the secure microcontroller's code but acts as a passive physical display signal capture device. In this way, if an attacker obtains the recovery phrase, they can replicate the wallet on any other platform and drain the stored assets without requiring subsequent physical access.
Scope of the incident and contingency measures
Trezor's commercial management confirmed that, although the device in question still needs to undergo thorough forensic analysis at their central laboratories, they have chosen to issue a preemptive public warning to prevent any financial losses. To date, the company has no record of any thefts directly attributable to this particular case.
CryptoBilis operated as an authorized distributor of hardware wallets in the East Asian region. Although Trezor indicated that the sales volume channeled through this company represented a small portion of its global operations, the seriousness of the issue prompted a comprehensive review. The company acknowledged that traditional tamper-evident seals and packaging are no longer sufficient barriers against advanced supply chain manipulation, and announced on October 13th a strict policy of reducing its external reseller network.
Precedents in the crypto hardware supply chain
The Trezor case is not an isolated incident within the physical security industry. Weeks earlier, in early October, similar manipulations were confirmed affecting devices from other manufacturers distributed by the same intermediary, CryptoBilis, where foreign components were detected inserted into the original motherboards. Independent investigations conducted by electronic security experts during the summer months had already reported alterations in classic models sold through unofficial social media channels.
To fully understand how the different storage levels work and how to effectively protect your private keys, you can consult the educational resources of Bit2Me AcademyThis section details the operational differences between cold wallets, hot wallets, and custodial solutions. Understanding your wallet's physical infrastructure is a fundamental step before proceeding. buy Bitcoin or any other crypto asset within a secure and regulated environment.
Operational recommendations for affected users
If you purchased a Trezor Safe 5 device or any other model through CryptoBilis or third-party platforms since last March, it is recommended to follow a strict mitigation protocol:
- Do not reuse the current recovery phrase: If the device was tampered with, the backup seed should be considered completely compromised.
- Transfer the funds immediately: Create a new portfolio in a non-exposed environment or use a custody platform regulated in the European Union to temporarily safeguard your assets.
- Verify the origin of the acquisition: Always purchase hardware devices directly from the original manufacturer or through verified entities that comply with the MiCA community regulations on technological security.
Staying up-to-date with the latest ecosystem news on reference portals such as Bit2Me News It allows you to react in time to emerging software and hardware vulnerabilities that could compromise the security of your funds.
FAQ
What should I do if I bought my Trezor through CryptoBilis?
You must immediately create a new wallet on an uncompromised device or in a secure environment and transfer all of your funds. Do not reuse the private key or recovery phrase generated on the suspicious device.
Does this vulnerability affect those who bought directly from the manufacturer?
Trezor has indicated that the suspected incidents are focused on units distributed through the reseller CryptoBilis and unauthorized channels. However, it is always recommended to check the physical seal and the integrity of the packaging before initialization.
Can the device's firmware detect these types of implants?
Not necessarily. This type of spy circuit is usually designed to capture screen signals or data input in parallel without altering the microcontroller's source code or invalidating the operating system's cryptographic signatures.
Security in the crypto ecosystem goes beyond software and encompasses the entire supply chain of physical devices. Identifying risks in storage components early allows users to protect their assets against increasingly sophisticated attack techniques.
Adopting responsible custody protocols and operating with transparent and properly regulated platforms under the European MiCA framework is the best defense to preserve the integrity of your digital assets in the long term.
Investing in cryptoassets is not fully regulated, may not be suitable for retail investors due to high volatility and there is a risk of losing all invested amounts.
Generative artificial intelligence tools were used to create this article.