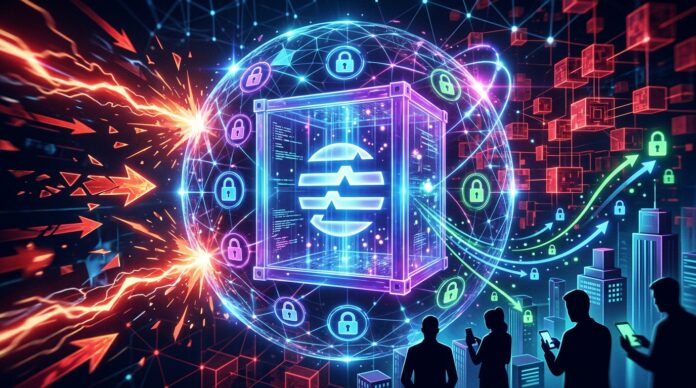
The Aptos Layer 1 network has implemented an optional encrypted mempool feature on its mainnet to protect users from abusive maximum extractable value (MEV) practices, such as front running and sandwich attacks. This tool hides the details of the transfers before they are executed.
The main objective of this technical update is to ensure that institutional traders, AI agents, and retail users can execute transactions without being exposed to aggressive arbitrage by automated bots.
Protection against the abusive extraction of MEV
The decentralized finance ecosystem has coexisted for years with the presence of bots that monitor the queue of pending trades. When a participant places an order on a traditional blockchain, any node or monitoring program can examine the parameters before they are confirmed: the assets involved, the trading volume, the limit price, and the smart contracts with which it interacts. This visibility allows specialized algorithms to execute orders immediately before or after the transaction to manipulate prices for their own benefit.
To address this scenario in their ecosystem, the Aptos' main network has activated an encrypted mempool This feature is optional. With this architecture, critical transaction information remains hidden during the block ordering process. This innovation aims to safeguard the value transferred by participants with large volumes and protect automated agents that rely on accurate contract executions.
The MEV phenomenon has had a considerable financial impact on other leading networks. According to industry data analyzed on Ethereum, sandwich attacks cost operators approximately $60 million over the 12 months leading up to October 2025. Meanwhile, on networks like Solana, Bitquery's analysis recorded nearly 6,9 million such attacks targeting 2,2 million wallets, generating around $29,7 million for bot operators over an eleven-month period.
How the encrypted mempool works in Aptos
This technology works directly on the user's device. By activating the option within a compatible wallet or application, the transaction's operational content is encrypted locally before being sent to the network. Sensitive parameters such as the amount transferred or the called contract remain unreadable, although the sender's address and gas fee are still visible so that validator nodes can verify the transaction's validity.
Once the encrypted packet enters the mempool, the network's validators work together to reach a consensus on the strict chronological order of transactions without knowing their contents. The security architecture relies on no single validator possessing the complete key or the ability to decrypt the order in isolation. To learn more about how distributed consensus works, you can consult resources at [link to resources]. Bit2Me Academy.
Once the block sequence is irrevocably fixed, the validators proceed in a coordinated manner to decrypt the transactions. At that precise moment, the transactions are executed on the blockchain ledger in the established order. Since predatory arbitrage bots cannot alter the order by knowing the amounts beforehand, they are unable to place orders in advance or insert speculative transactions.
Costs and technical considerations of the tool
Integrating advanced cryptographic layers entails certain compromises in terms of resources and processing speed. In the case of Aptos, the technical specifications indicate that transactions using the encrypted mempool will incur a minimum gas fee equivalent to twice the network's usual minimum. This increase reflects the extra computational effort required for joint decryption among the validator nodes.
Furthermore, performance analyses in test environments with 50 validator nodes show an addition of approximately 20 milliseconds per block compared to the conventional consensus system. This small latency represents a manageable cost in exchange for ensuring the temporal privacy of financial instructions, especially for treasuries and high-volume decentralized applications that require stable execution.
Unlike other solutions on the market, Aptos does not delegate sequencing or decryption to external entities or privileged block builders. In protocols like Gnosis Chain, encryption relies on committees through networks like Shutter, while Ethereum typically uses private methods like Flashbots Protect to mitigate public scrutiny. Aptos entrusts the entire validation, sequencing, and decryption cycle exclusively to its own set of native validators, simplifying the chain of trust.
Implications for the ecosystem and the European framework
Mitigating abusive market execution (MEV) is key to the maturation of decentralized infrastructures toward institutional standards. In the context of the European Union and the implementation of the MiCA Regulation, the operational integrity of crypto-asset markets and protection against price manipulation are among the supervisory priorities. Technologies that prevent market abuse at the settlement layer provide functional clarity for operators.
Aptos (APT) continues to expand its technical offering to attract institutional flows and autonomous agent applications. If you closely follow the technological evolution of this ecosystem and are looking to build your portfolio with high-performance technology-based assets, you can explore the options available on the platform. Bit2Me news or consult the guides for Buy Apartments in a safe and regulated manner.
With these measures, the network developers seek to make mempool privacy a viable standard against excessive value extraction, setting a precedent on how layer 1 architectures can natively solve fair sequencing challenges without sacrificing the decentralization of their validators.
FAQ
What is the maximum extractable value or MEV?
Maximum extractable value (MEV) refers to the profit validators or search bots can make by deliberately altering, including, or excluding the order of pending transactions in a block. It often negatively impacts users by worsening their execution prices on decentralized exchanges.
Is it mandatory to use the encrypted mempool in Aptos?
No, the feature is entirely optional. Users and developers can choose whether to send their transactions via the traditional transparent channel or enable temporary encryption. Transfers using this protection will incur a slightly higher minimum gas fee due to the additional computing power required for decryption.
Who can decrypt the transaction data before it is ordered?
No single node or validator can decrypt the transaction in isolation. The parameters remain unreadable in the mempool until the block order is finalized. Only then do the validators coordinate the joint decryption of the transactions before proceeding with their final execution on the blockchain.
The integration of the encrypted mempool in Aptos represents a significant technical advancement in the fight against on-chain transaction manipulation. By neutralizing sandwich attacks and abusive arbitrage through native cryptography, the network strengthens operational safeguards for both developers and large operators in the crypto ecosystem.
Investing in cryptoassets is not fully regulated, may not be suitable for retail investors due to high volatility and there is a risk of losing all invested amounts.
Generative artificial intelligence tools were used to create this article.